
Certified Security. Proven Data Protection. For Over 20 Years.
Companies, public authorities, and organizations with high security requirements need more than just promises.
For more than two decades, TeamDrive has stood for verifiable security, data protection, and legal compliance – independently audited and consistently implemented across architecture, operations, and organization.
This page gives you a clear overview of all relevant certificates, seals, and compliance standards that qualify TeamDrive for professional use.
As a customer, you can meet all the compliance requirements you need with TeamDrive – we provide the solution and support you.
TeamDrive is ISO/IEC 27001:2022 certified.
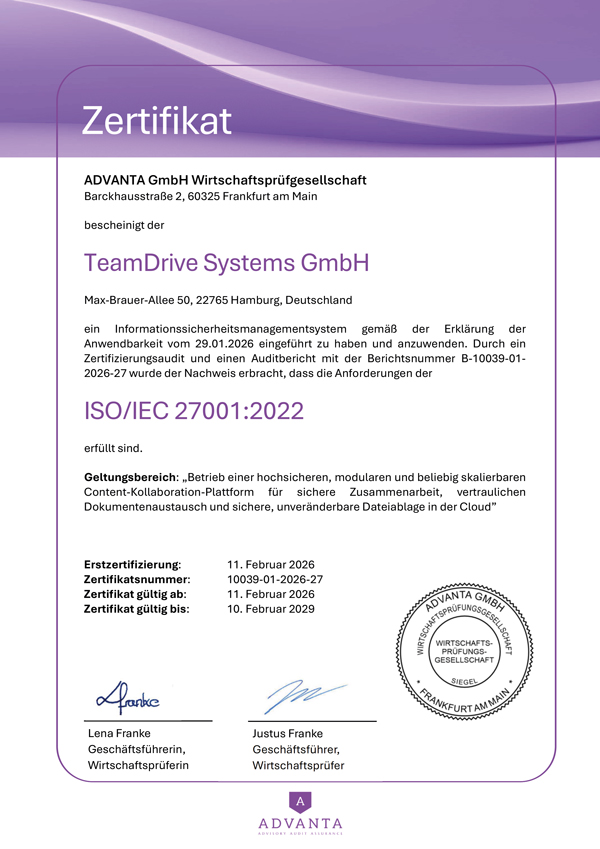
TeamDrive Systems has successfully achieved ISO/IEC 27001:2022 certification. The certificate confirms that our Information Security Management System fully meets the requirements of the international standard.
Our new ITSM and GRC systems were entirely developed and implemented in-house. As a result, information security is not just a formal process, but a lived part of our daily work. Every team member understands the relevant standards and applies them consistently. We thank our entire team for their strong commitment and for firmly embedding information security into TeamDrive’s DNA.
Detlef Schmuck, Founder and CEO, TeamDrive Systems GmbH
Certified Hosting in Accordance with ISO/IEC 27001 and BSI C5
- Hosting in German Data Centers
- No Data Transfers to Third Countries
- No Access by Foreign Authorities
The data of the TeamDrive Cloud Service is stored exclusively in IONOS SE data centers located in Frankfurt, Germany. The infrastructure meets the highest security and compliance standards and is certified according to ISO/IEC 27001 and BSI C5.
All data is encrypted on your device using AES-256 end-to-end encryption before transmission and remains encrypted at all times during storage and synchronization. The keys remain exclusively under the control of the users – neither TeamDrive nor the hosting provider has access to them. This security concept has been regularly audited since 2005.
The cloud service fully complies with all requirements of the General Data Protection Regulation (GDPR). Customers receive a Data Processing Agreement (DPA) as well as access to relevant certifications and audit reports of the infrastructure. The systems are continuously audited and adapted to new requirements, such as those defined in the IT-Grundschutz Compendium of the German Federal Office for Information Security (BSI).
Important:
Only you hold the keys to decrypt your data – not TeamDrive.
At a Glance: Why TeamDrive Is Secure
✔ ISO/IEC 27001:2022 certified
✔ Continuously audited and recertified since 2005
✔ End-to-end encrypted with a zero-knowledge architecture
✔ GDPR-compliant and developed with privacy by design
✔ Hosting exclusively in German data centers certified to ISO/IEC 27001 and BSI C5
Key Certifications & Seals of Quality
🇪🇺 European Privacy Seal (EuroPriSe)
TeamDrive is regularly audited by EuroPriSe.
The seal confirms the consistent implementation of data protection and data security under GDPR – including:
- Full end-to-end encryption
- Zero-knowledge platform
- Suitability for professionals bound by confidentiality
🇩🇪 Alliance for Cyber Security (BSI)
TeamDrive is an active participant in the Alliance for Cyber Security of the German Federal Office for Information Security (BSI).
Goal: strengthening cyber resilience in Germany through transparent security standards.
International & Industry-Specific Compliance
Healthcare & HIPAA
TeamDrive supports healthcare organizations in securely processing sensitive data in compliance with HIPAA, in particular through:
- Strong encryption
- Secure private cloud structures
- Zero-knowledge principle
Hospital Future Fund (KHZF)
TeamDrive is suitable for projects under the KHZF, including in the following areas:
- Electronic documentation
- IT security
- Secure digital collaboration
TISAX® (Automotive Industry)
For data with high and very high protection requirements, TeamDrive meets the requirements of TISAX®:
- Secure collaboration along the supply chain
- Protection of sensitive development and production data
ITAR (US Export Control)
TeamDrive supports compliance with ITAR requirements for the electronic processing of technical data:
- Strict access separation
- Comprehensive logging
- Protection against unauthorized third-party access
CCPA (California, USA)
TeamDrive also supports the requirements of the California Consumer Privacy Act:
- Protection of personal data
- Implementation of access, deletion, and opt-out rights
- Market-location principle, regardless of company headquarters
GoBD (Germany)
TeamDrive supports GoBD compliance through:
- Immutable storage
- Full traceability (audit trail)
- Audit-proof document archiving
Certification History: Security with Substance
TeamDrive has had its solution regularly audited and recertified since 2005.
Earlier audits were conducted, among others, by the Independent Centre for Privacy Protection Schleswig-Holstein.
Documented audits:
- Short assessment (2005)
- Recertifications in 2007, 2009, 2011, 2013, and 2016
- Ongoing GDPR audits to this day
Transparent Documentation for Audits & Tenders
TeamDrive provides all relevant documentation in a structured format:
- Certificates & seals
- Data Processing Agreement (DPA)
- Technical and organizational measures (TOMs)
- Security & compliance documentation
This allows audits, procurement procedures, and internal reviews to be carried out quickly and without friction.
Additional Seals and Certifications
Who Is This Compliance Particularly Relevant For?
Professionals Subject to Confidentiality Obligations under Section 203 of the German Criminal Code (StGB)
- Doctors, lawyers, tax advisors, pastors, etc.
- All TeamDrive employees are bound by the confidentiality requirements of Section 203 StGB
- End-to-end encrypted communication and storage
- All encryption keys remain under the control of the professional bound by confidentiality
- Only encrypted data is stored in the cloud; cloud administrators have no access
Public Authorities & Regulated Industries
- Long-standing legal certainty and stability
- Transparent security and organizational processes
- Proven use in sensitive environments
Management & Procurement
- Reduction of liability and compliance risks
- Independent certifications as a basis for decision-making
- Usable in tenders, audits, and procurement procedures
IT & Security Professionals
- End-to-end encryption of all data
- Zero-knowledge architecture (no access by the provider)
- Fine-grained rights and role models
- Audit-ready, traceable logging
Data Protection & Legal
- GDPR-compliant data processing
- Data processing agreements under Art. 28 GDPR
- Clear separation of customer and system data
- Data storage within the European legal framework
Security at TeamDrive Is Not a Feature – It’s the Foundation
Compliance is not a one-time achievement.
TeamDrive continuously develops its security, data protection, and organizational measures to consistently meet current legal and technical requirements.
The result:
A highly secure, GDPR-compliant document management solution for organizations
that cannot afford to compromise on data protection and security.